
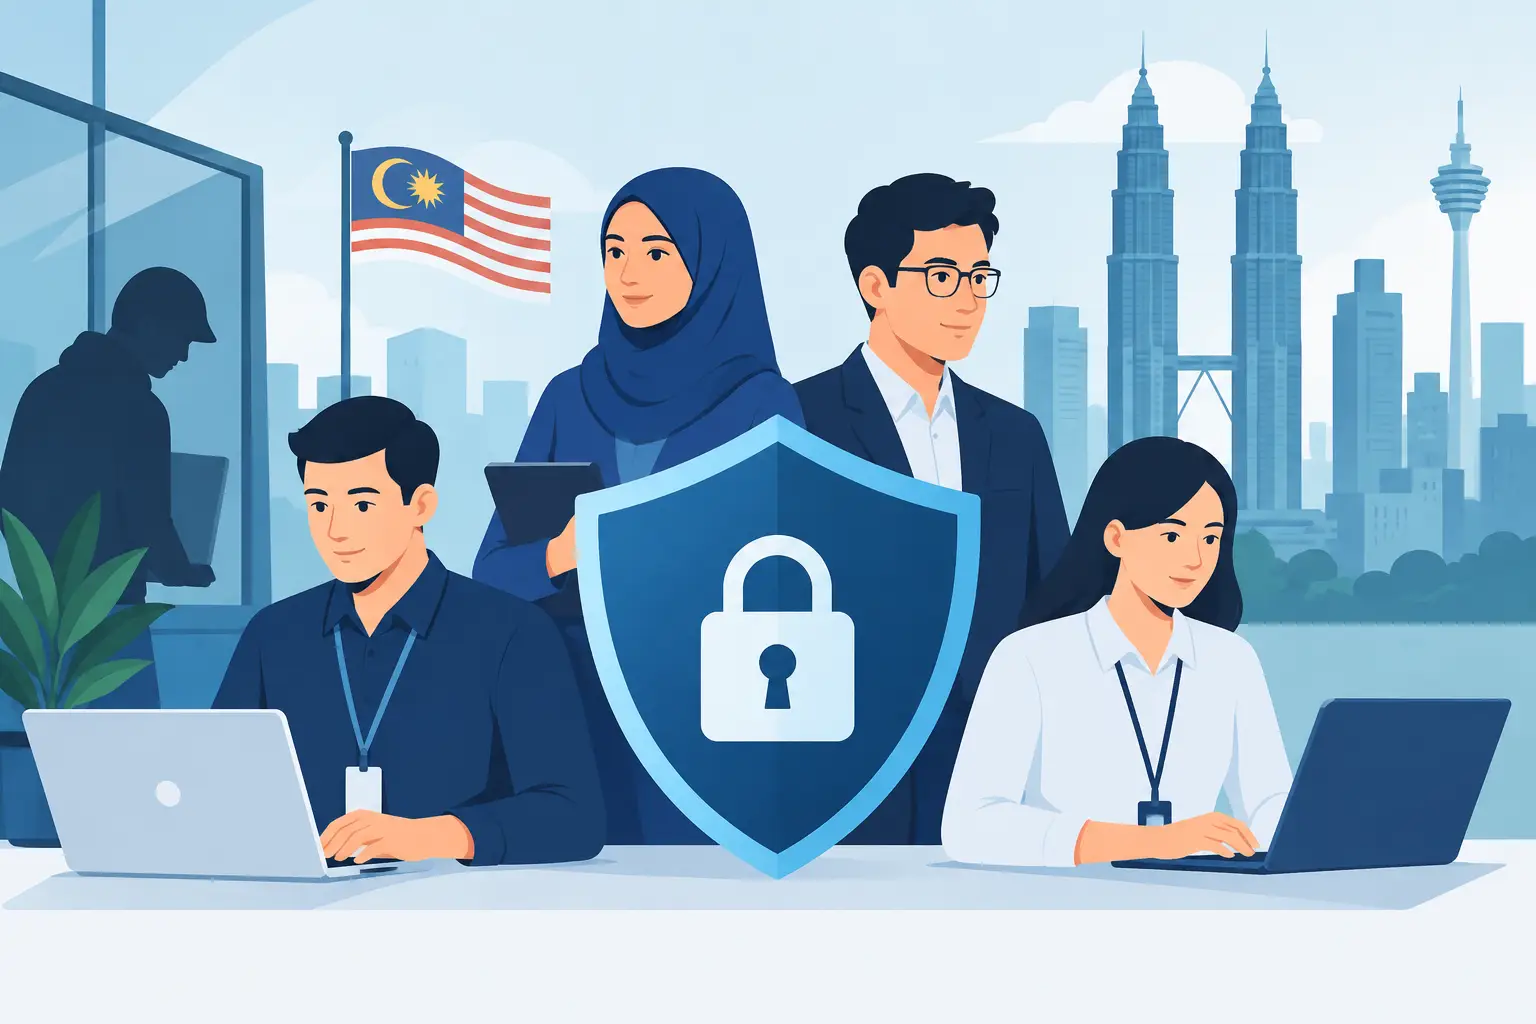
A trusted employee can create significant exposure long before a formal incident is discovered. Customer records copied before resignation, false expense claims, undisclosed conflicts of interest, manipulated supplier payments and the misuse of confidential files often begin as small control failures. Effective insider threat prevention helps Malaysian employers identify these risks earlier, investigate them fairly and protect the business without treating every employee as a suspect.
The risk is not limited to deliberate fraud. An employee may send commercially sensitive information to a personal e-mail account for convenience, approve a vendor linked to a family member, or retain system access after changing roles. Intent matters when investigating misconduct, but the damage can occur regardless. That is why prevention must combine reliable screening, clear controls, proportionate oversight and a lawful response process.
Why insider threats deserve board-level attention
Insider risk sits at the intersection of people, access and opportunity. Employees, temporary staff, contractors, consultants and even departing personnel may have legitimate access to systems, assets, financial information or customer data. Where duties are poorly separated or access is not reviewed, one individual can potentially initiate, approve and conceal an improper transaction.
For SMEs, the issue can be especially acute. A small finance or operations team may depend heavily on a few trusted people, with limited segregation of duties and little capacity for independent review. Larger organisations face a different challenge: complex systems, multiple locations and extensive third-party workforces can make unusual activity harder to see.
The commercial consequences extend beyond a direct financial loss. A data leak can damage customer confidence. A fraudulent appointment can expose the organisation to litigation, regulatory scrutiny or an operational failure. If the matter involves senior personnel, directors or business partners, reputational harm can reach suppliers, insurers, lenders and investors.
Insider threat prevention starts before employment
The strongest time to reduce insider risk is before access, authority and trust are granted. A curriculum vitae, interview performance or professional reference alone cannot establish whether a candidate is suitable for a role with access to funds, confidential information, vulnerable customers or strategic decisions.
Pre-employment screening should be proportionate to the role and conducted through lawful, confidential processes. For relevant positions, employers may need to verify identity, employment history, qualifications and professional references. Depending on the nature of the appointment and applicable requirements, further checks may include civil litigation, industrial court records, regulatory blacklists, financial-probity indicators, directorships, security concerns and criminal or Interpol-related searches.
The purpose is not to exclude candidates on the basis of untested information. It is to identify material inconsistencies, undisclosed risks and claims that require clarification before an appointment is approved. A candidate who has overstated a qualification may present a different risk from one who failed to disclose a directorship connected to a competing supplier. Decision-makers need verified facts, context and a documented basis for action.
Screening should also apply beyond permanent recruitment. Contractors, outsourced personnel, senior consultants and staff assigned through agencies can receive access equivalent to employees. A risk-based process should reflect the access they will hold, the duration of the engagement and the sensitivity of the work.
Match screening depth to the role
A standard administrative role and a finance controller role should not be assessed in the same way. Positions with payment authority, procurement influence, privileged technology access, customer data access or responsibility for regulated activity generally warrant deeper review. Senior hires and directors also require careful due diligence because their decisions can bind the organisation commercially and legally.
This approach avoids two common mistakes: under-screening high-risk appointments and collecting excessive information for lower-risk roles. The objective is defensible risk management, not indiscriminate surveillance.
Build controls around the moments where misconduct occurs
Screening reduces the chance of admitting a known or undisclosed risk, but it cannot predict every future action. Financial pressure, workplace grievances, weak supervision and opportunity can change circumstances after a person joins. Practical internal controls are therefore essential.
Access should be granted according to job need, not convenience. Review who can view, download, amend or approve sensitive information and transactions. Remove access promptly when a person changes role, starts extended leave or leaves the business. Dormant accounts and shared passwords create avoidable exposure because accountability becomes unclear.
For financial processes, separate the ability to create a supplier, approve an invoice and release a payment wherever possible. Independent checks of new bank details, unusual payment patterns and changes to vendor information can prevent a single individual from redirecting funds. In smaller businesses where complete separation is difficult, owner or management review can provide an effective compensating control.
The following warning signs deserve measured attention, particularly when several occur together:
- repeated resistance to leave, hand over duties or accept review of their work;
- unexplained changes to supplier details, customer records or payment instructions;
- unusual downloading, printing or forwarding of confidential material;
- undisclosed relationships with vendors, competitors or customers; and
- expenses, claims or transactions that sit outside established patterns.
These indicators are not proof of wrongdoing. They are reasons to verify facts, preserve relevant records and consider whether controls need to be strengthened. A sudden allegation or confrontational questioning can compromise an investigation and expose the employer to unnecessary employment risk.
Make reporting safe, specific and credible
Employees often see concerns before management does. They may notice a colleague bypassing an approval step, using a personal account for company documents or showing unusual interest in sensitive records. Yet staff will stay silent if they believe reporting will lead to retaliation, gossip or no meaningful action.
A clear reporting route should explain what can be reported, who receives concerns, how confidentiality will be handled and what protection is available to those raising issues in good faith. Managers should know not to promise absolute secrecy, as an investigation may require disclosure on a need-to-know basis. They should, however, treat reports discreetly and prevent unnecessary circulation of allegations.
The organisation also needs a consistent response. Record the concern, assess immediate risks, secure relevant systems and documents, and appoint appropriate people to investigate. Where an allegation involves a senior manager, finance approver or internal investigator, independence becomes particularly important. External support may be appropriate where specialist verification, neutrality or sensitive fact-finding is required.
Use post-employment screening and review where risk changes
Risk management should not stop on an employee’s first day. Post-employment screening, periodic declarations and role-based reviews can be appropriate when someone moves into a sensitive position, receives new signing authority or takes on procurement, finance or data responsibilities.
Employers should set this expectation from the outset through contracts, policies and privacy notices. Any continued screening must have a clear business purpose, use relevant information only and follow applicable legal and data-protection obligations. In Malaysia, handling personal data demands particular care: collection, use, retention and disclosure should be controlled, justified and protected.
A proportionate review can also help identify conflicts that emerge over time. An employee may become a director of another company, establish a side business or develop a close relationship with a supplier after joining. Not every outside interest is improper. The risk depends on the role, the relationship and whether the interest has been declared and managed.
Protect the investigation as carefully as the evidence
When concerns arise, organisations can cause further damage by acting too quickly. Suspending system access without preserving evidence, alerting the subject before key records are secured or allowing untrained managers to conduct interviews can make a defensible investigation harder.
A sensible initial response is to limit access only where necessary, preserve logs and records, establish a clear chain of custody, and separate facts from assumptions. The individual should be treated fairly, given an opportunity to respond at the appropriate stage and managed in line with internal policy and employment obligations. Confidentiality protects both the organisation and the person under review.
Turn screening findings into better decisions
A screening report is most useful when it supports a defined decision. HR, legal, finance and operational leaders should agree in advance which findings require clarification, escalation, additional controls or rejection. This prevents inconsistent treatment and reduces the risk that material findings are overlooked because a hiring manager is under pressure to fill a vacancy.
Angel Checks supports organisations with confidential, fact-based screening that can help assess candidates, directors, business partners and other parties before high-consequence decisions are made. Verification is most valuable when it forms part of a wider control environment, rather than being treated as a one-off recruitment formality.
The aim of insider threat prevention is not to create a culture of suspicion. It is to make trust accountable: verify material facts, restrict sensitive access appropriately, listen when concerns are raised and act on evidence. Organisations that do this consistently give honest employees greater protection while making fraud, theft and misuse of information far more difficult to conceal.

Leave A Comment